/المدونة
Sharing the Latest Tech Innovations, UX Secrets, and Digital Media Tools.
Discover the world of technology and innovation with our updated articles.
2026-08-19
Web Development

Eng. Mohamed MostafaBack-End Developer
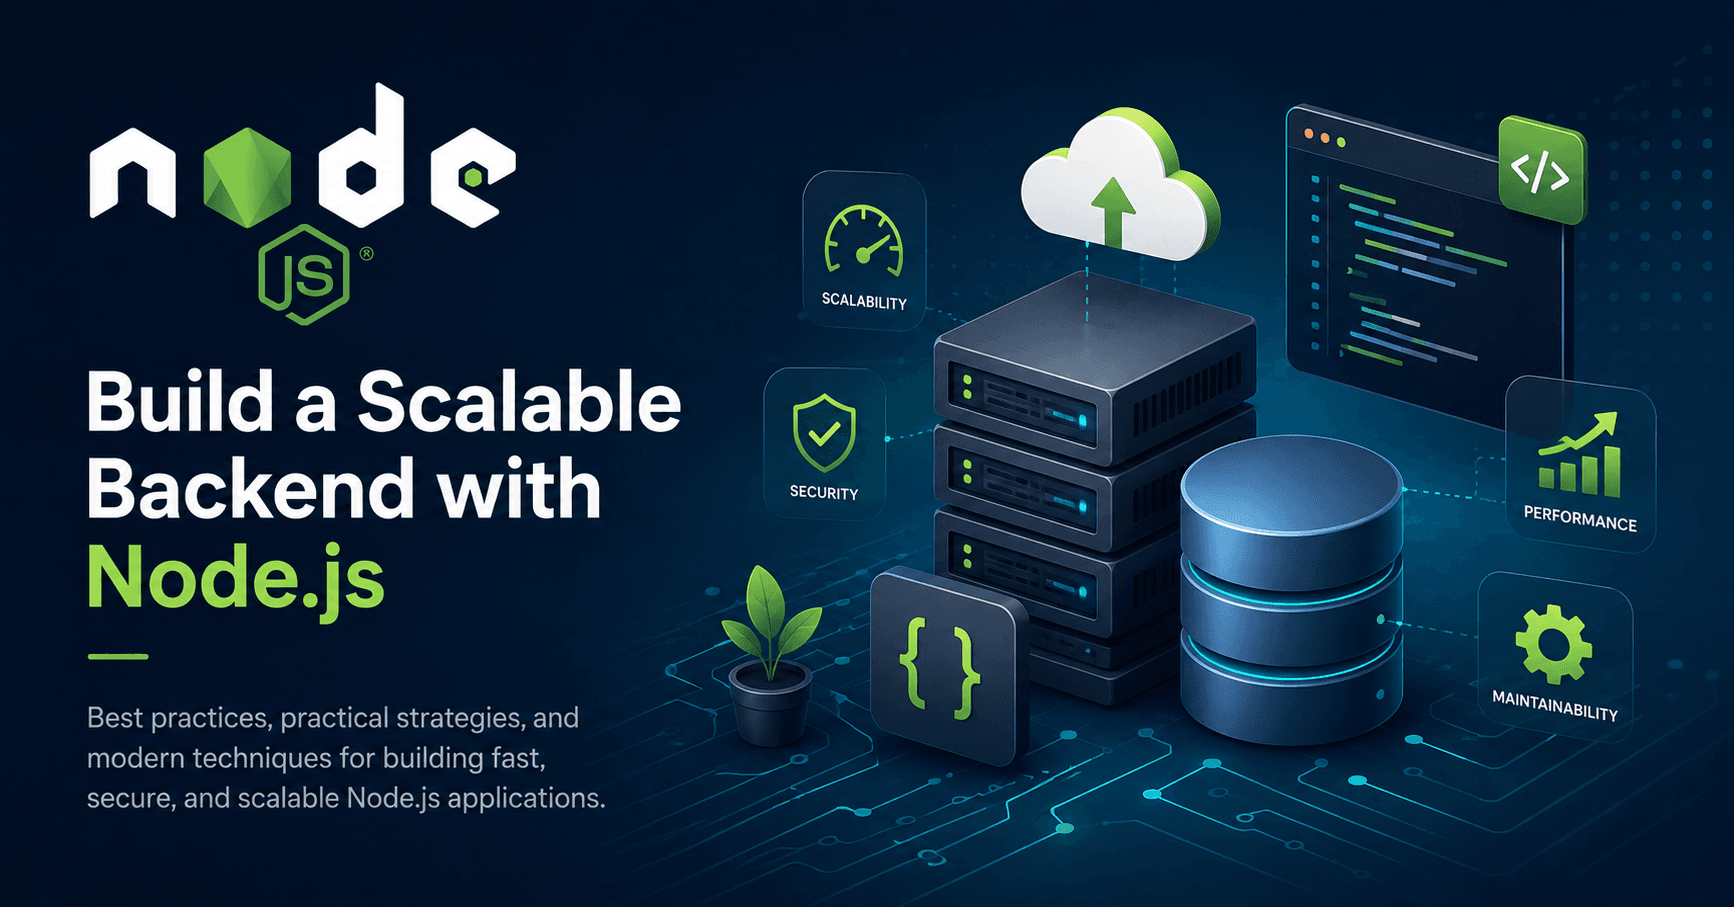
Designing a Scalable Backend Architecture with Node.js
Learn key architectural patterns, database optimizations, and security practices to build highly scalable Node.js backend systems.
Why Backend Architecture Matters for Growth
- A well-designed backend architecture isolates complex business logic from external delivery mechanisms and infrastructure choices, ensuring that the application remains adaptable when core technical requirements inevitably shift over time.
- Implementing structural boundaries early in development prevents software systems from degrading into unmaintainable codebases where minor functional updates frequently trigger widespread regression bugs across unrelated modules.
- Establishing clear operational roles allows large engineering teams to work concurrently on separate application components without introducing code conflict bottlenecks or breaking existing integration points.
Structuring Layered Node.js Applications Efficiently
- Separating concerns into distinct controllers, service layers, and data repositories ensures that incoming HTTP requests are validated and routed without cluttering core business operations with transport-specific protocol details.
- Service modules manage application-specific workflow logic independently of database querying code, making the core software behavior significantly easier to unit test without requiring live database network connections.
- Data repositories abstract database access operations completely, enabling engineering teams to optimize raw database queries or swap storage infrastructure without modifying higher-level business rules.
Designing Stateless Systems for Horizontal Scaling
- True backend horizontal scalability requires keeping application nodes stateless so that traffic management systems can seamlessly distribute incoming client traffic across multiple server instances dynamically.
- Externalizing active session state and temporary data to fast key-value memory stores like Redis prevents instance-bound sessions from restricting scale-out application deployment strategies.
- Implementing non-blocking background workers for computational operations ensures the primary event loop remains responsive and ready to process incoming network requests without latency spikes.
Database Optimization Caching and Query Efficiency
- Unoptimized database access patterns quickly become the primary performance bottleneck in web applications as concurrent user traffic increases beyond initial launch expectations.
- Implementing strategic database indexing and pagination strategies minimizes memory overhead and drastically reduces response execution time for data-heavy API endpoints during peak load periods.
- Caching frequently accessed read-heavy payload data reduces database cluster stress, ensuring fast responses for users while dramatically reducing overall server operational resource consumption.
Centralized Error Handling and Request Validation
- Validating all incoming API payload parameters before executing business logic prevents corrupted data from entering the application context and reduces unexpected runtime execution failures.
- A centralized error-handling middleware standardizes error responses across the entire system, ensuring consistent response schemas while preventing internal diagnostic details from leaking to potential attackers.
- Implementing structured JSON logging mechanisms allows development teams to trace execution pathways, monitor API health metrics, and identify runtime failures efficiently in production environments.
Robust Security Protocols and Identity Authorization
- Separating user authentication mechanisms from authorization logic allows system operators to enforce fine-grained role-based access control policies cleanly across diverse application resources and administrative workflows.
- Securing API deployments requires implementing robust token management, password hashing, and strict CORS configuration to protect sensitive application endpoints from unauthorized access vectors.
- Applying strict API rate-limiting rules at network gateways prevents denial-of-service attempts and protects database infrastructure from automated brute-force exploitation patterns.